Access controls
and a clear audit trail
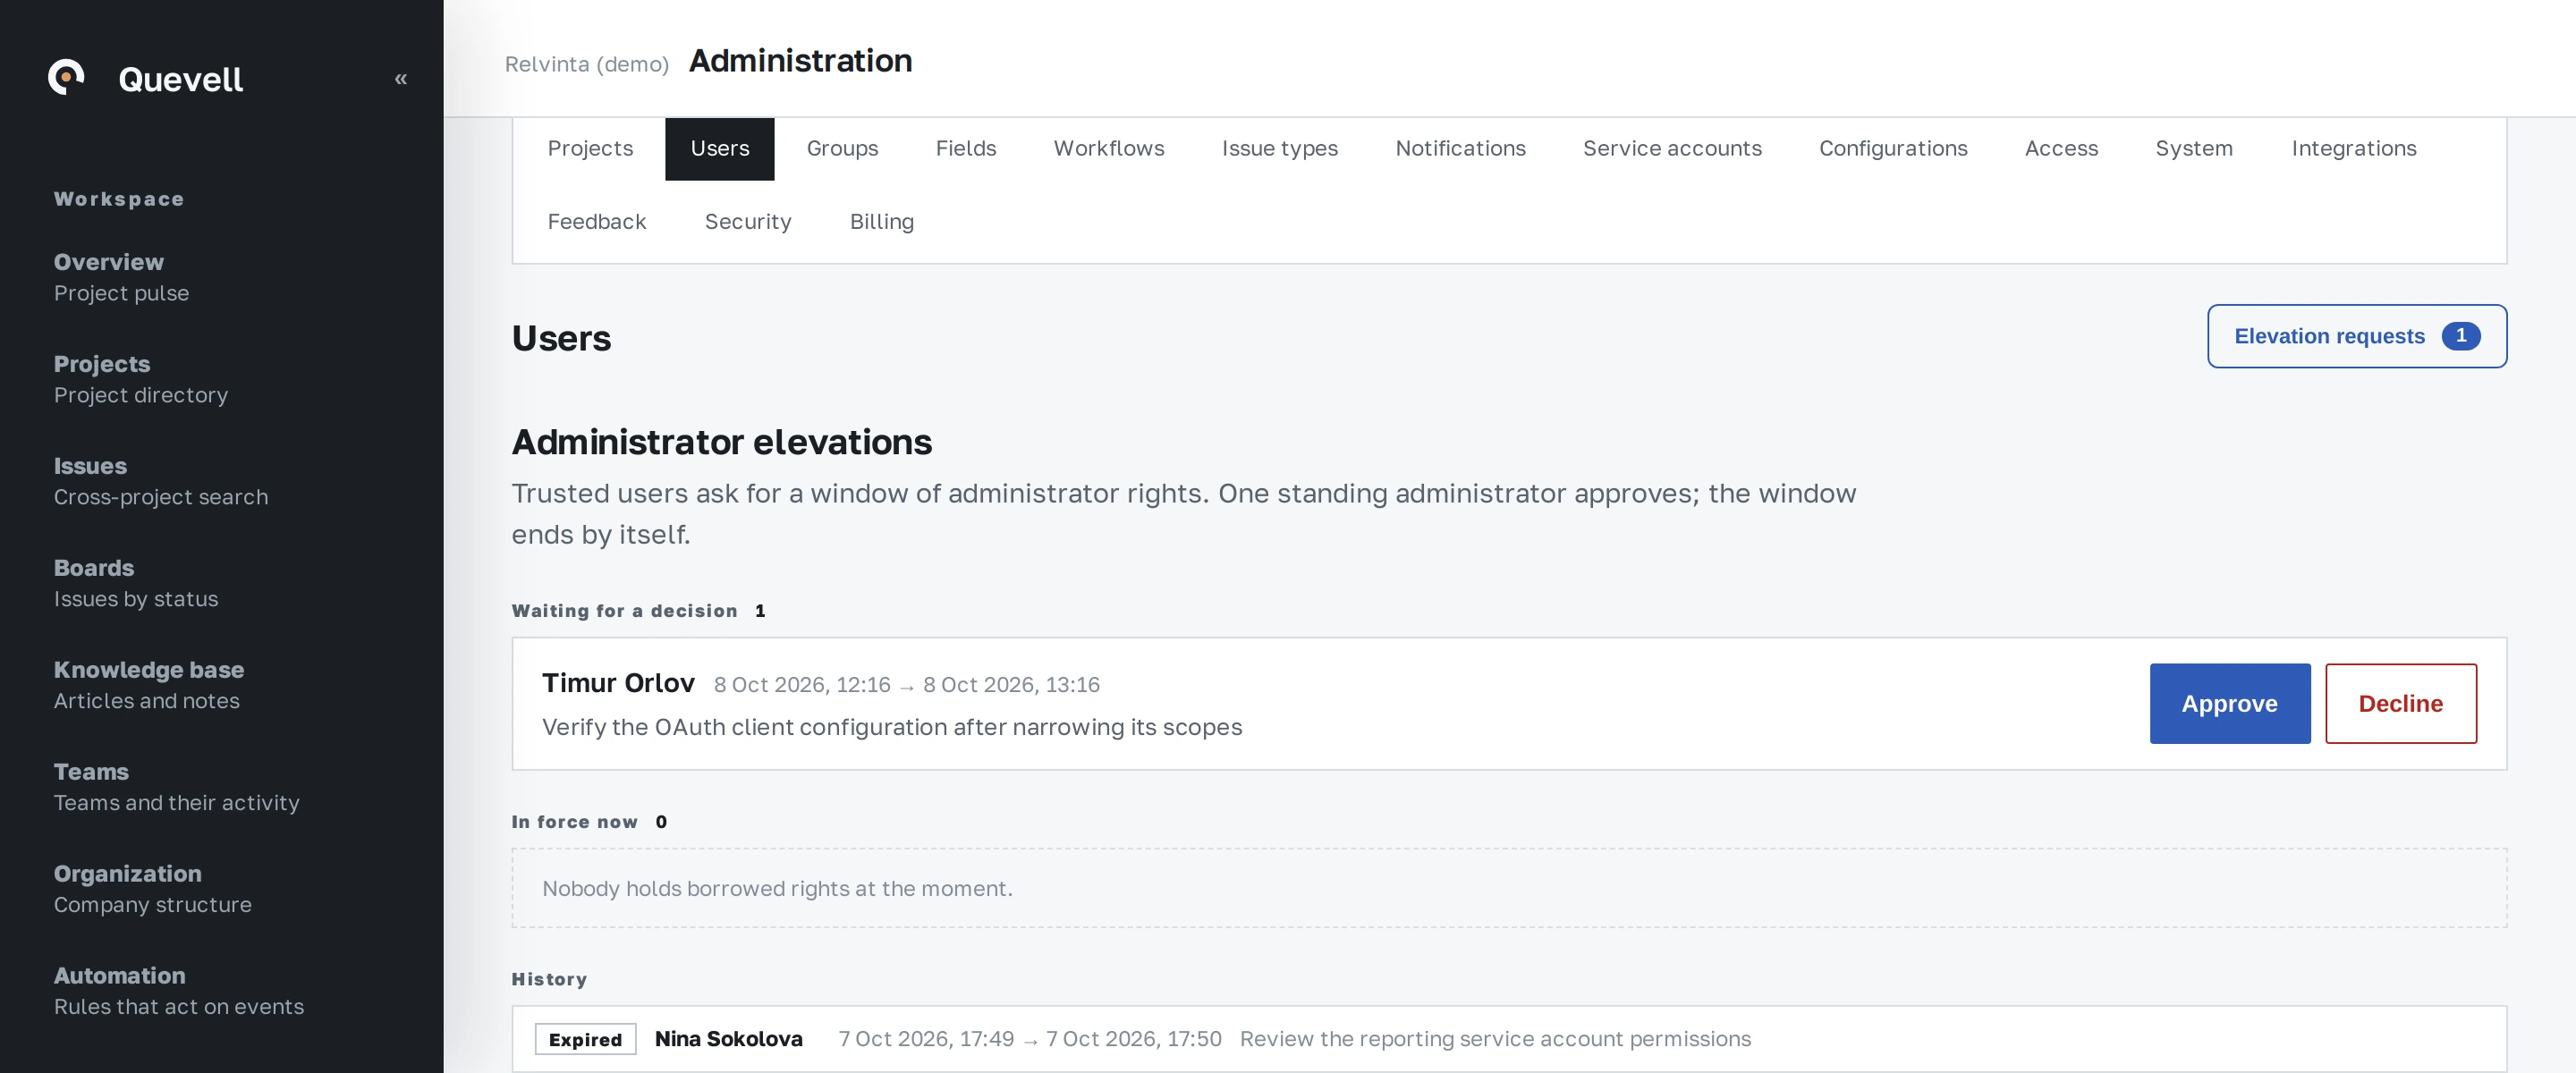
Project roles and issue security control who can work with the data. Administrator rights can be granted for a limited period, and Handover and access transfers work when someone leaves. Issue history records changes to an issue; the company Audit trail records access and configuration changes.
Protect an issue within a shared project
Set a security level on an issue within the project access model. Its grants select users, roles and groups from those allowed into the project. Service accounts pass the same checks.
Read the documentation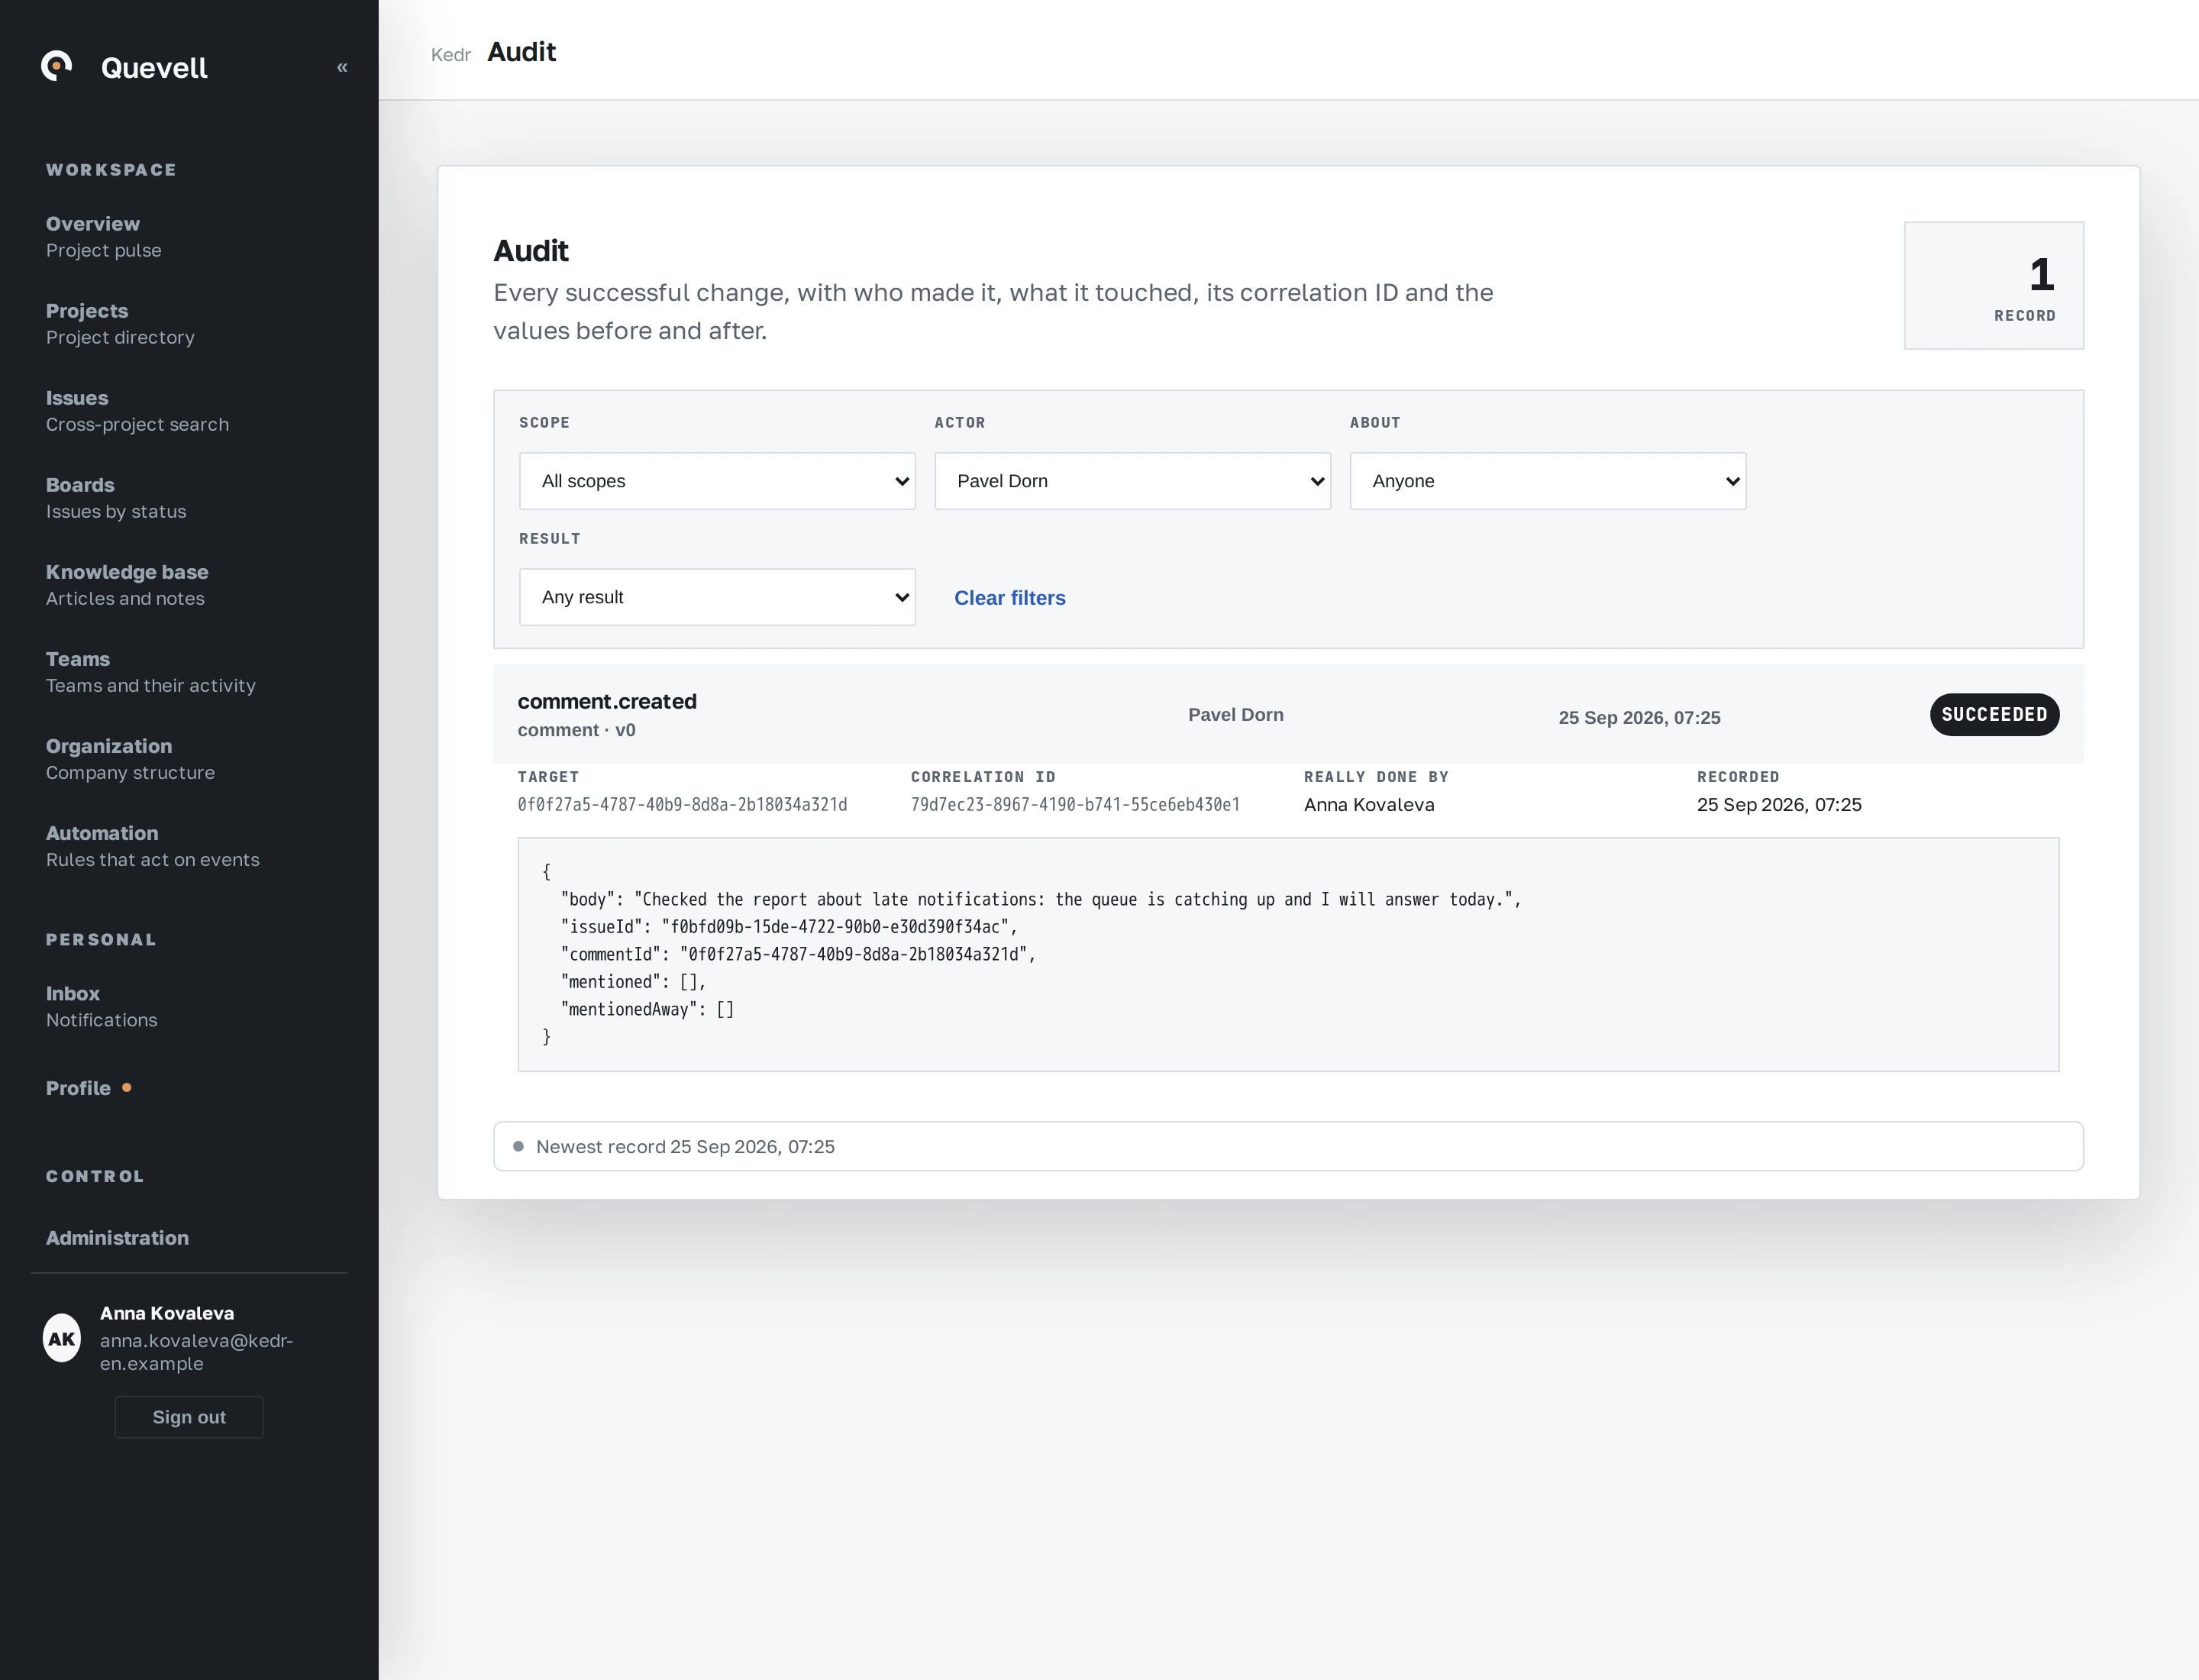
Project roles define permissions
A person receives a project role directly or through a group. The role grants actions such as viewing, creating and editing issues or administering the project. Issue security further narrows who can access an issue.
Read the documentationAdministrator rights for a set period
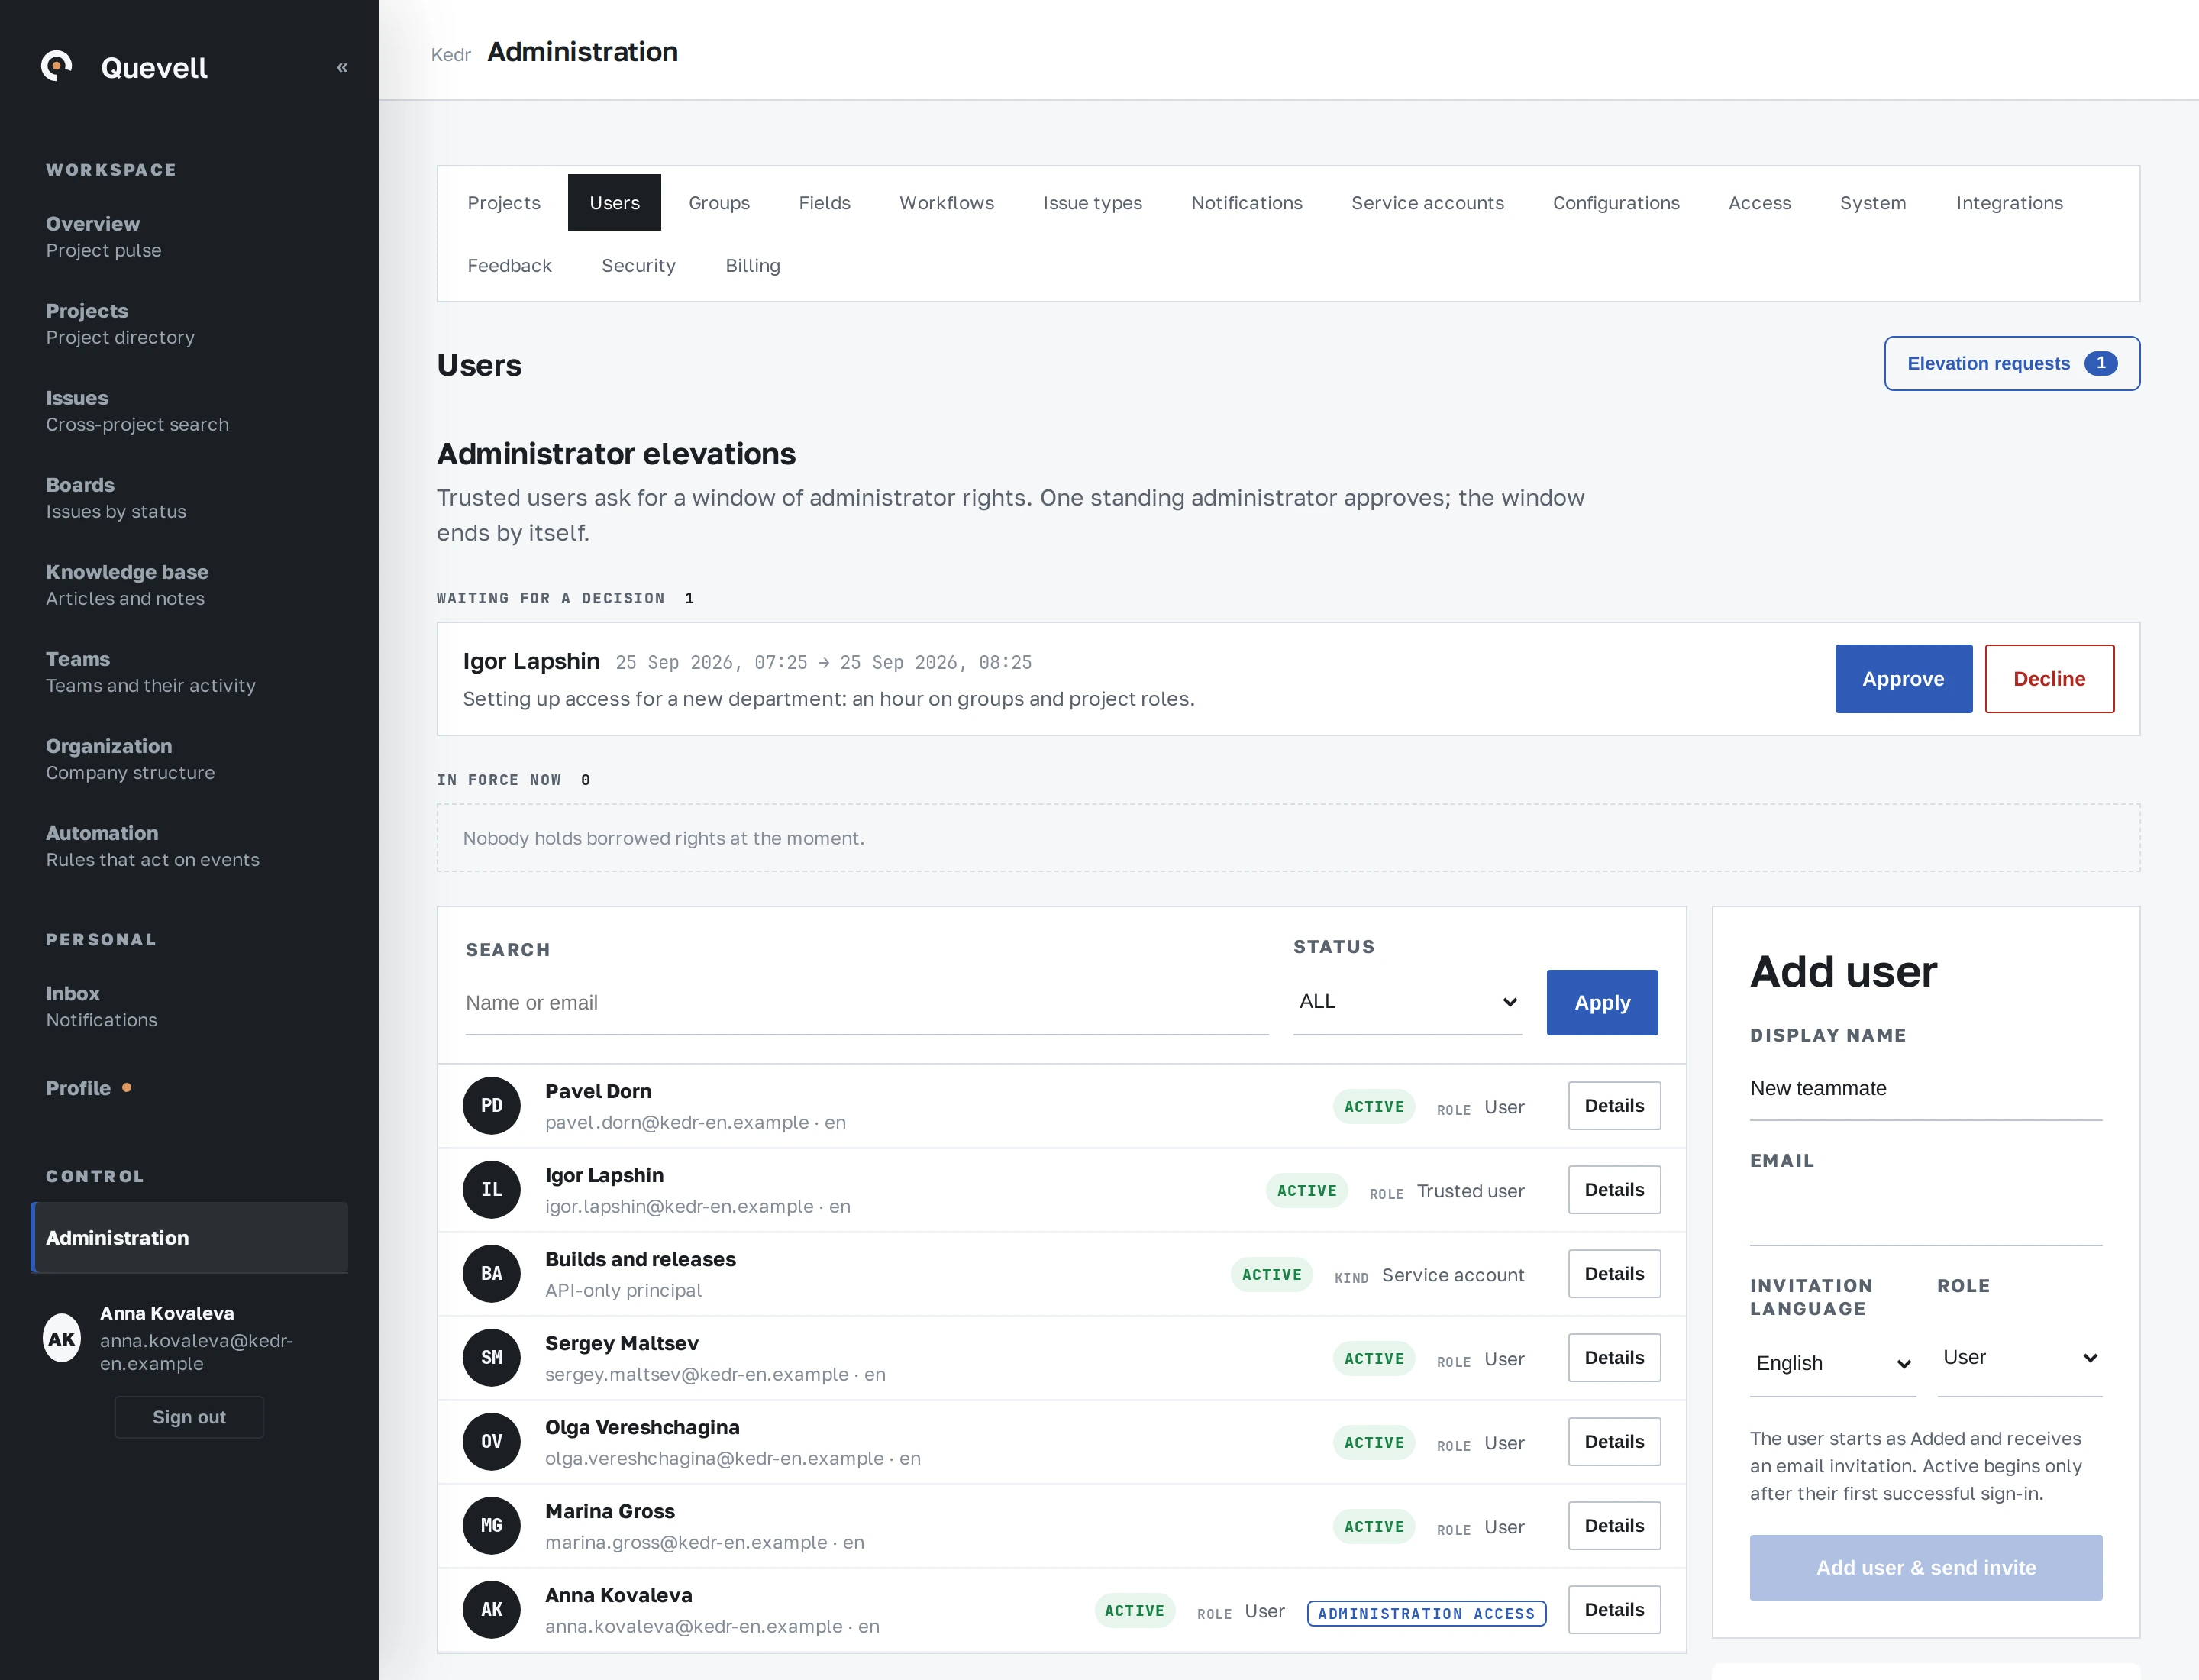
A Trusted user requests Administrator rights with a reason and a start and end time. A standing administrator decides. Borrowed rights expire with the window and do not allow the holder to grant those rights to others.
Read the documentation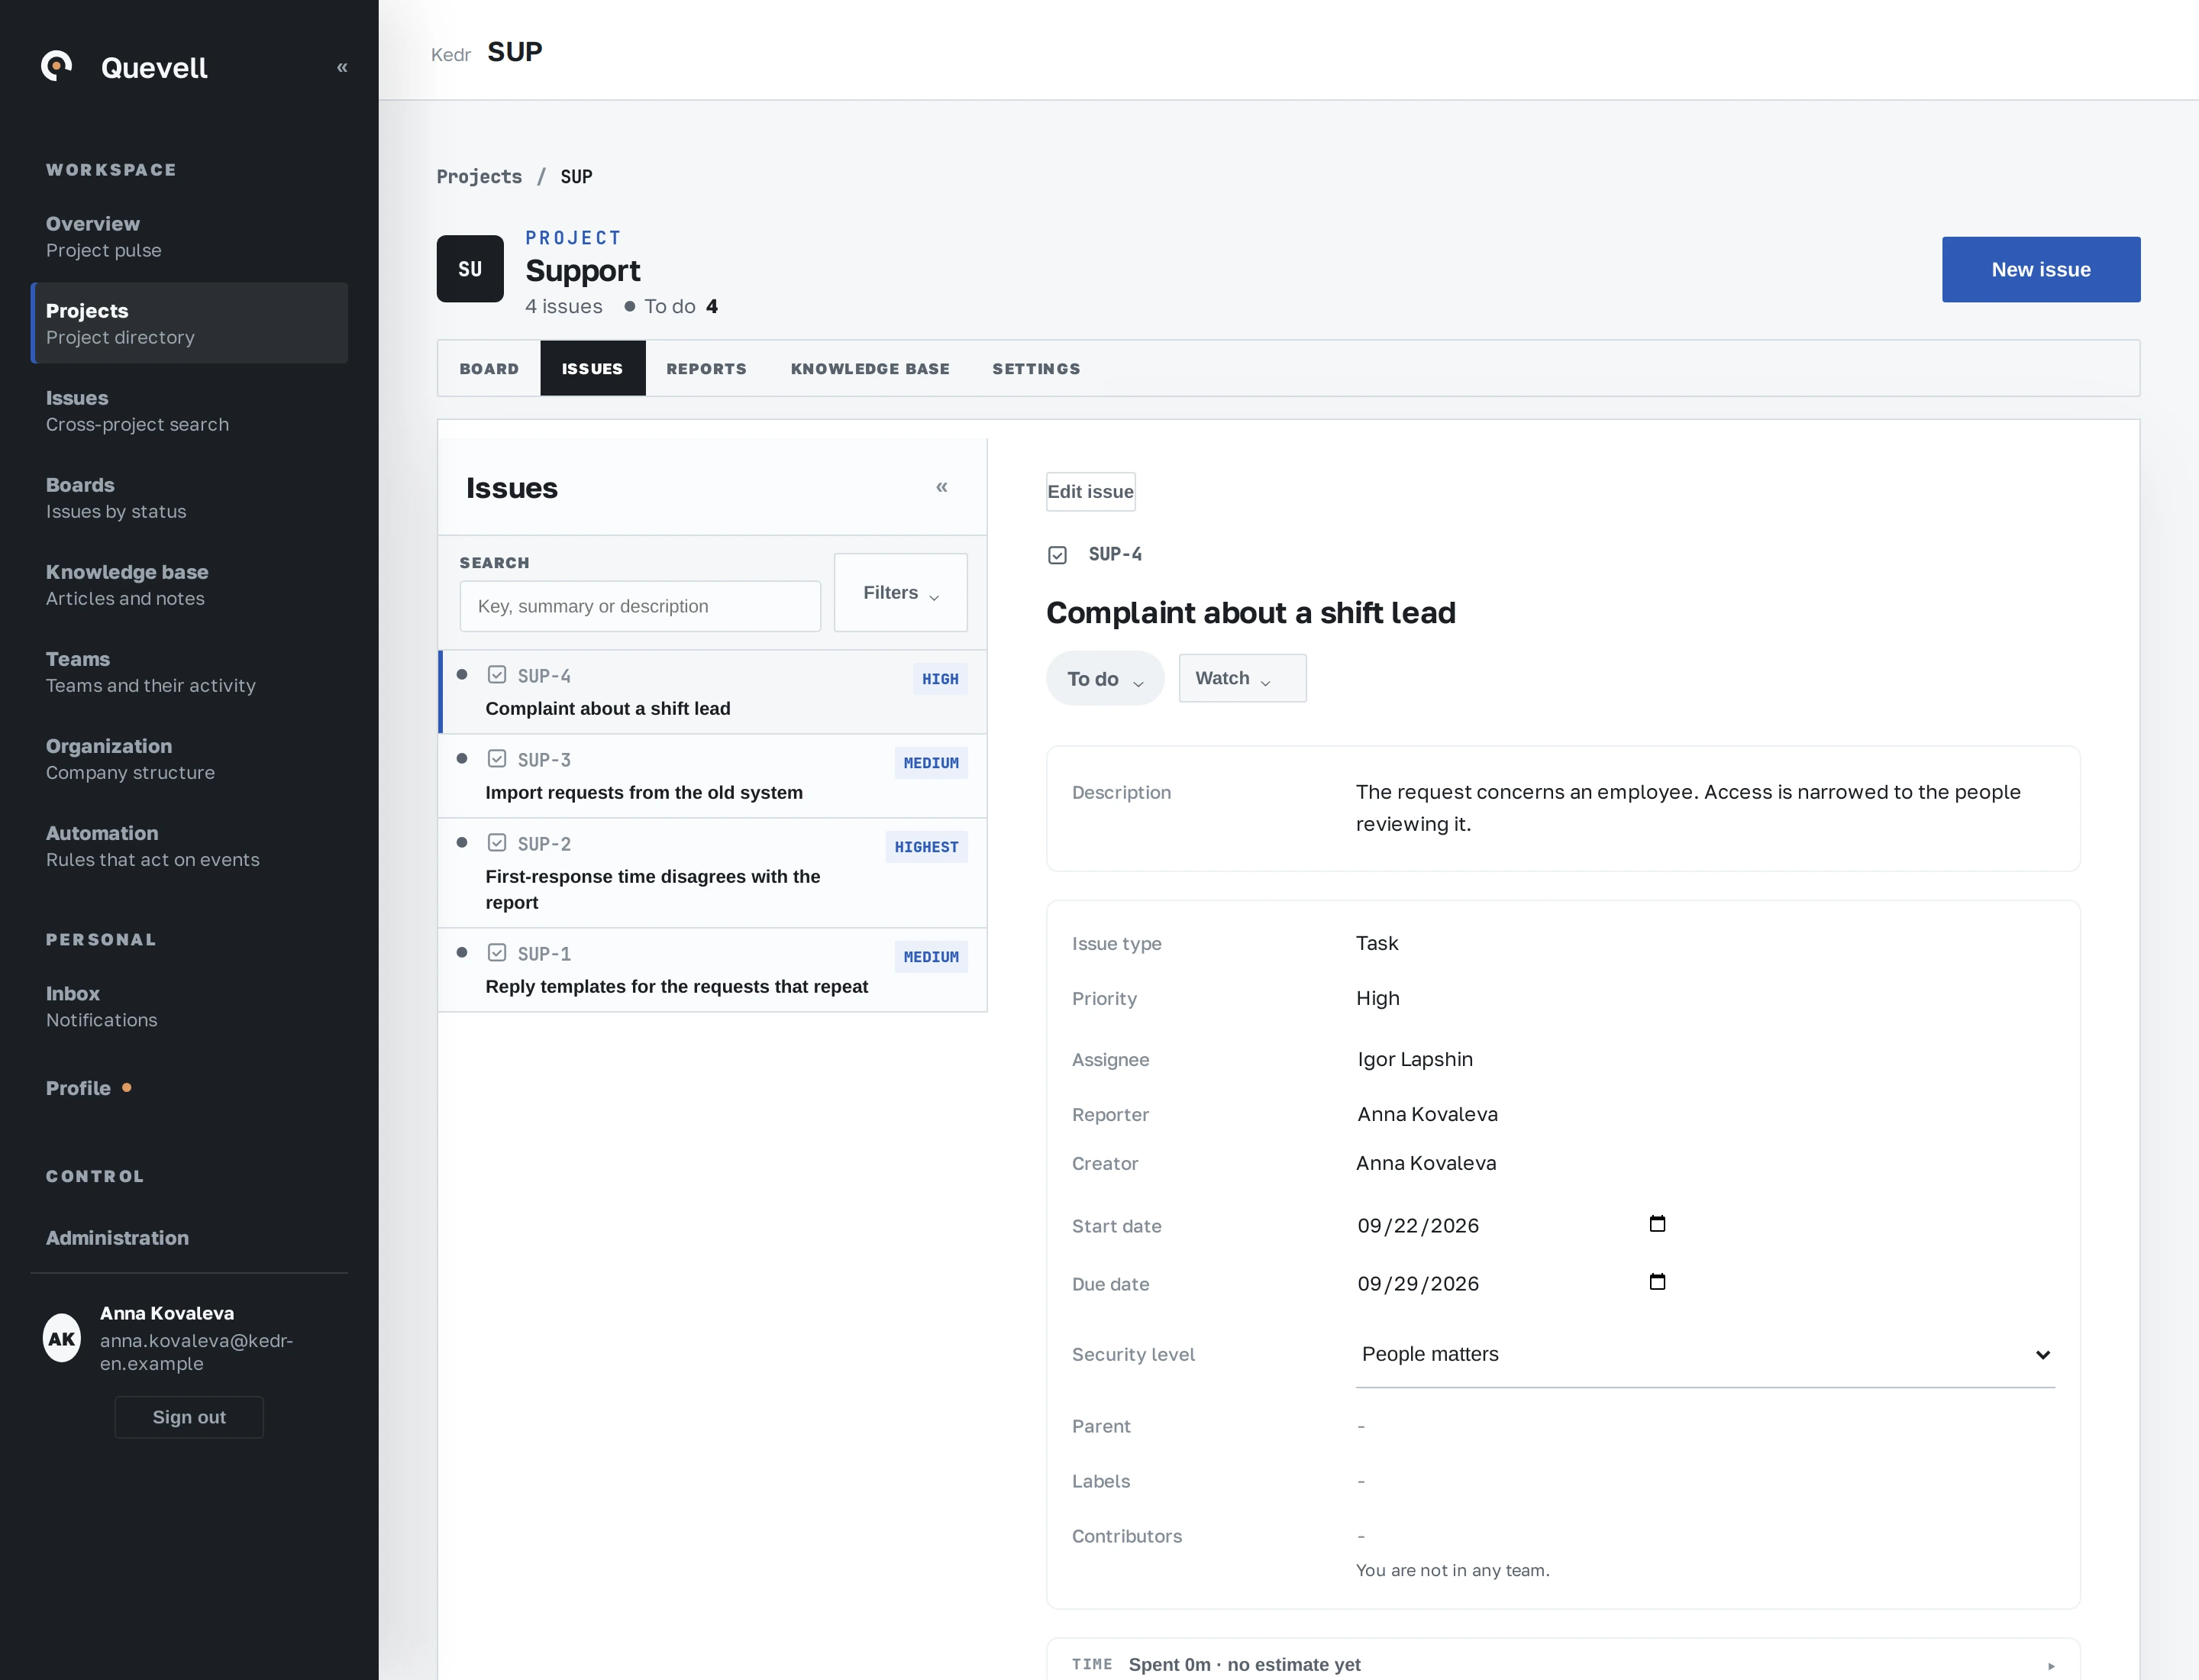
Time-limited Administrator rights
A Trusted user requests an administration window with a reason. A different standing administrator decides. Administrator rights expire when the approved window ends and cannot be used to grant those rights to others.
Keep the record through a handover
Handover and access shows what passes to the successor: assignments, roles and other work. Deactivation closes a user's access. Issue history and the company's audit trail retain authorship and changes.
Read the documentation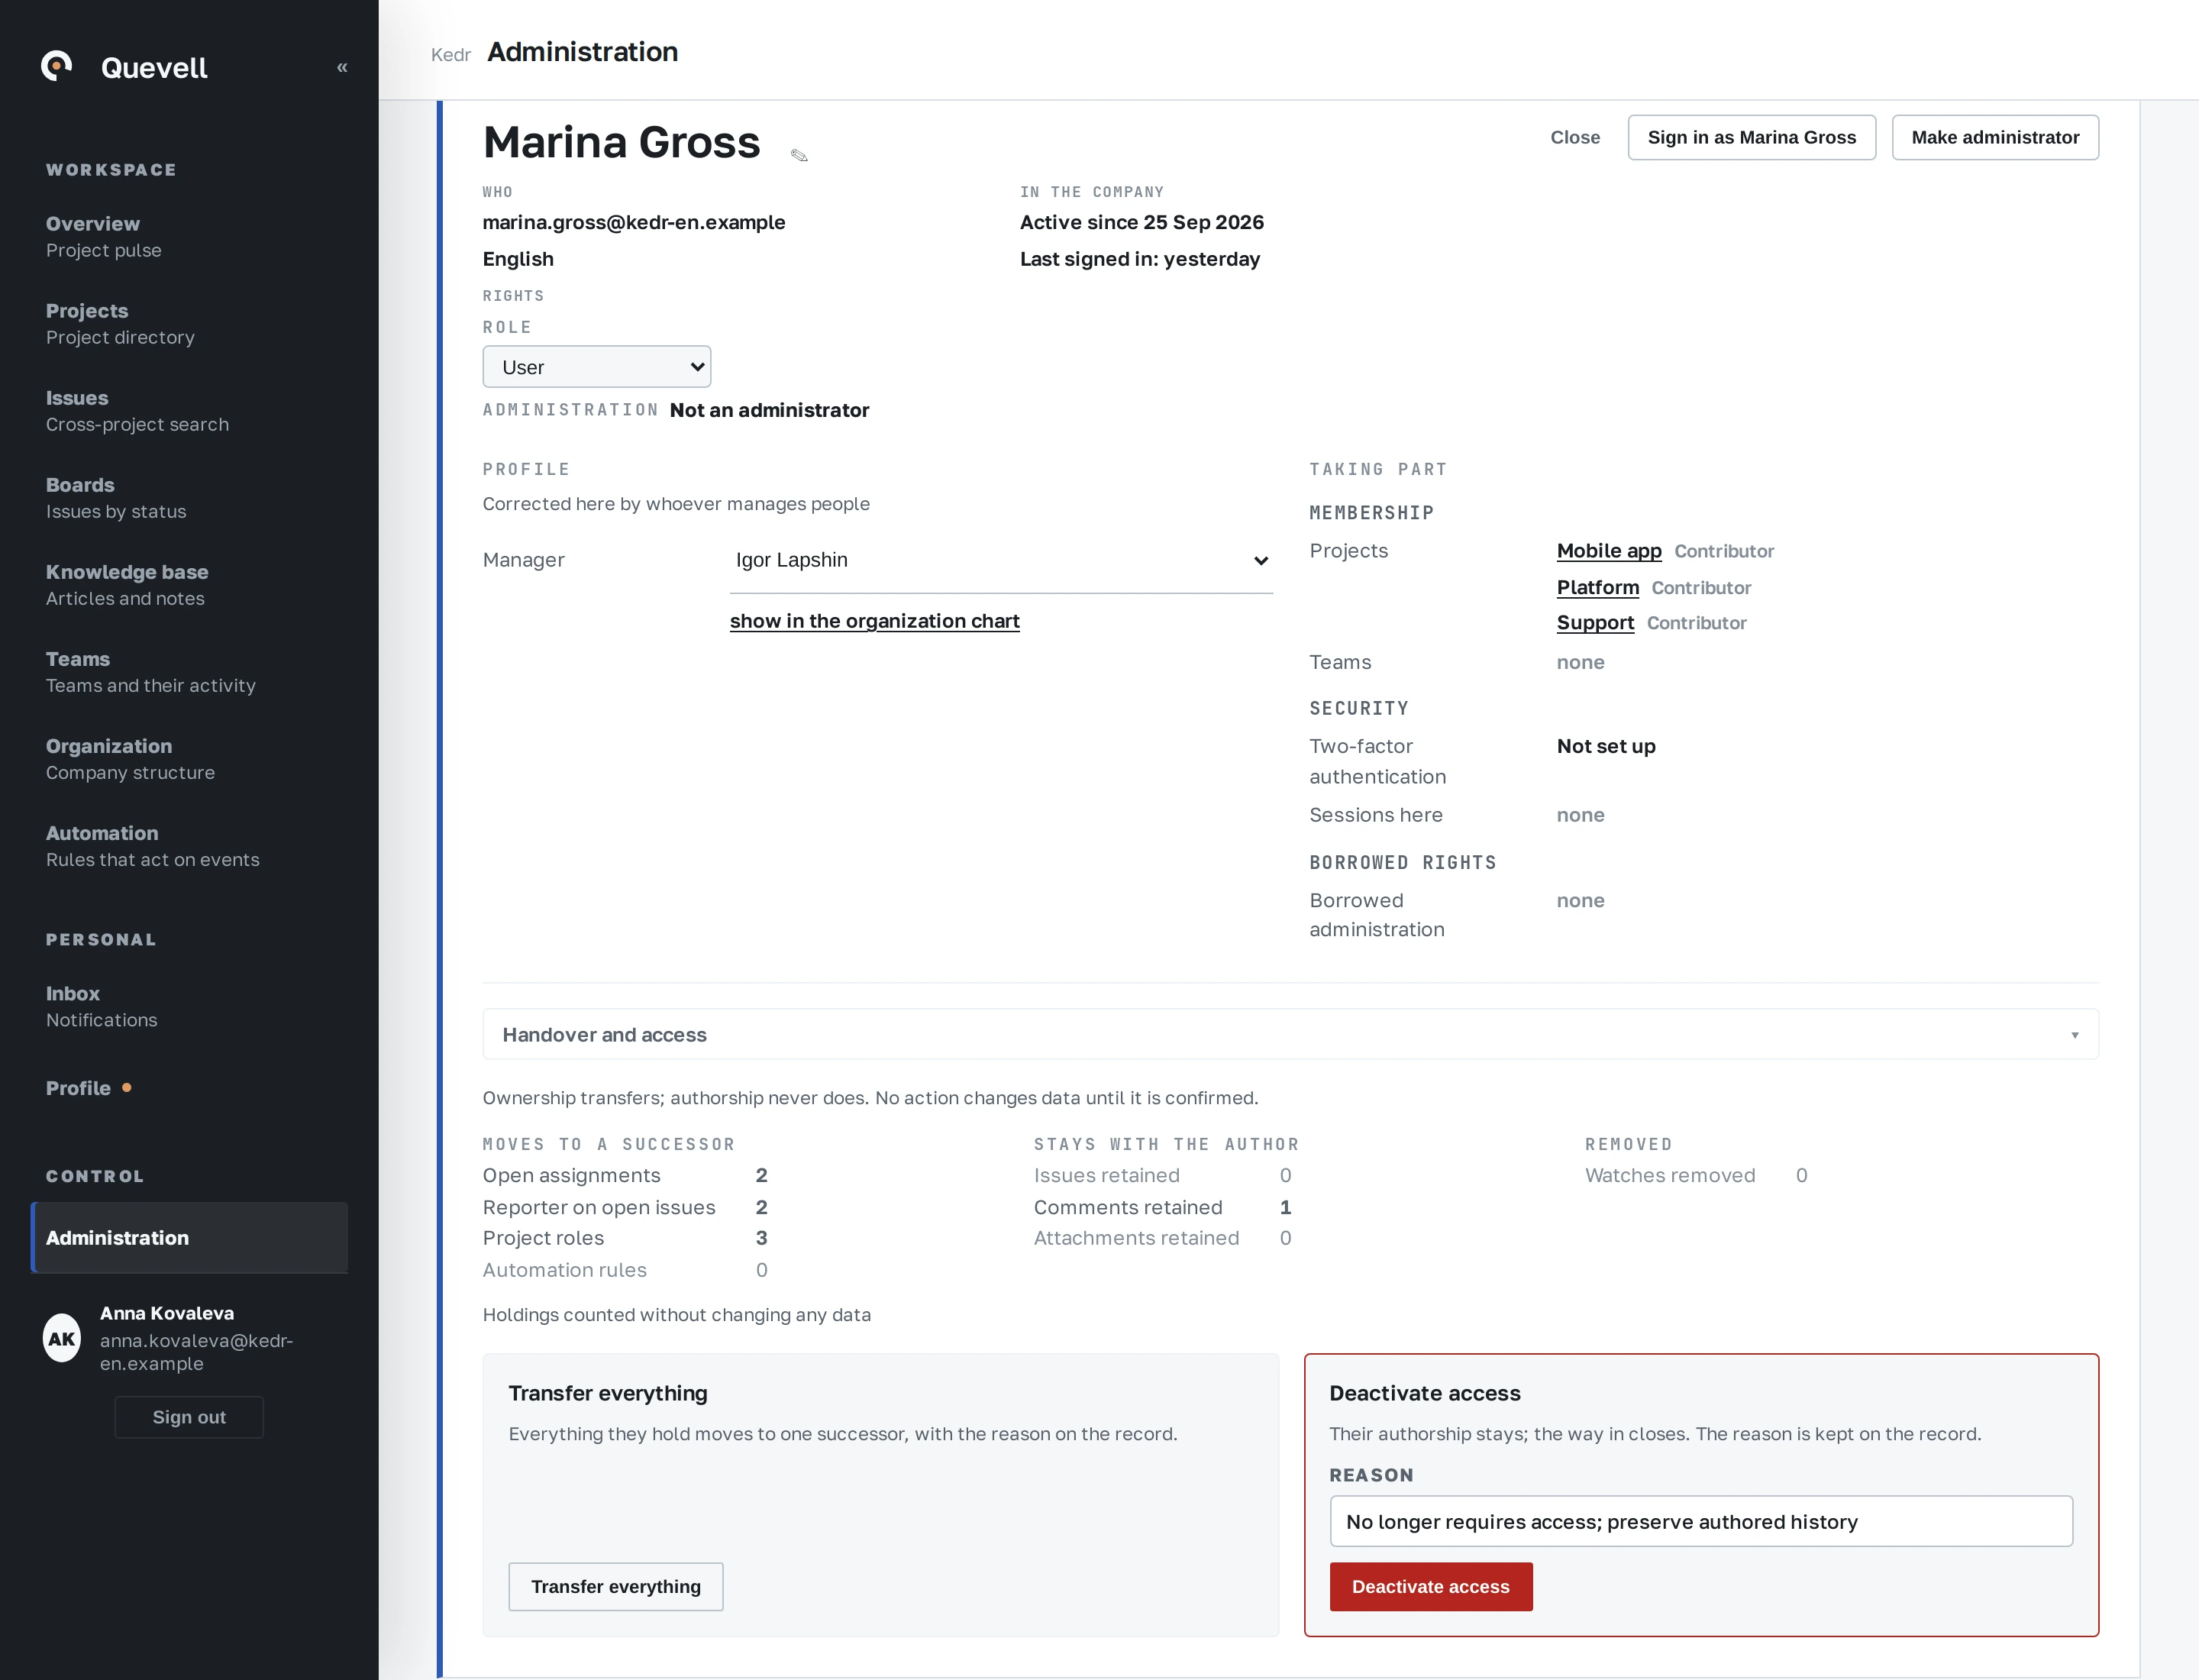
Try it with your own work
30 calendar days, up to 10 seats, the full product.