Security is a set
of specific limits
Who signs in, what they see, how elevated access is granted and what remains on the record. These are facts about Quevell today, with links to the details.
Sign-in and credentials
Sign-in requires a confirmed email address. Passwords are stored as Argon2id hashes. Two-factor authentication uses an authenticator app and backup codes; a company can require it for its users.
Sessions are revocable on the server. Service accounts use separately issued, revocable tokens with scoped permissions.
Project, issue and administration
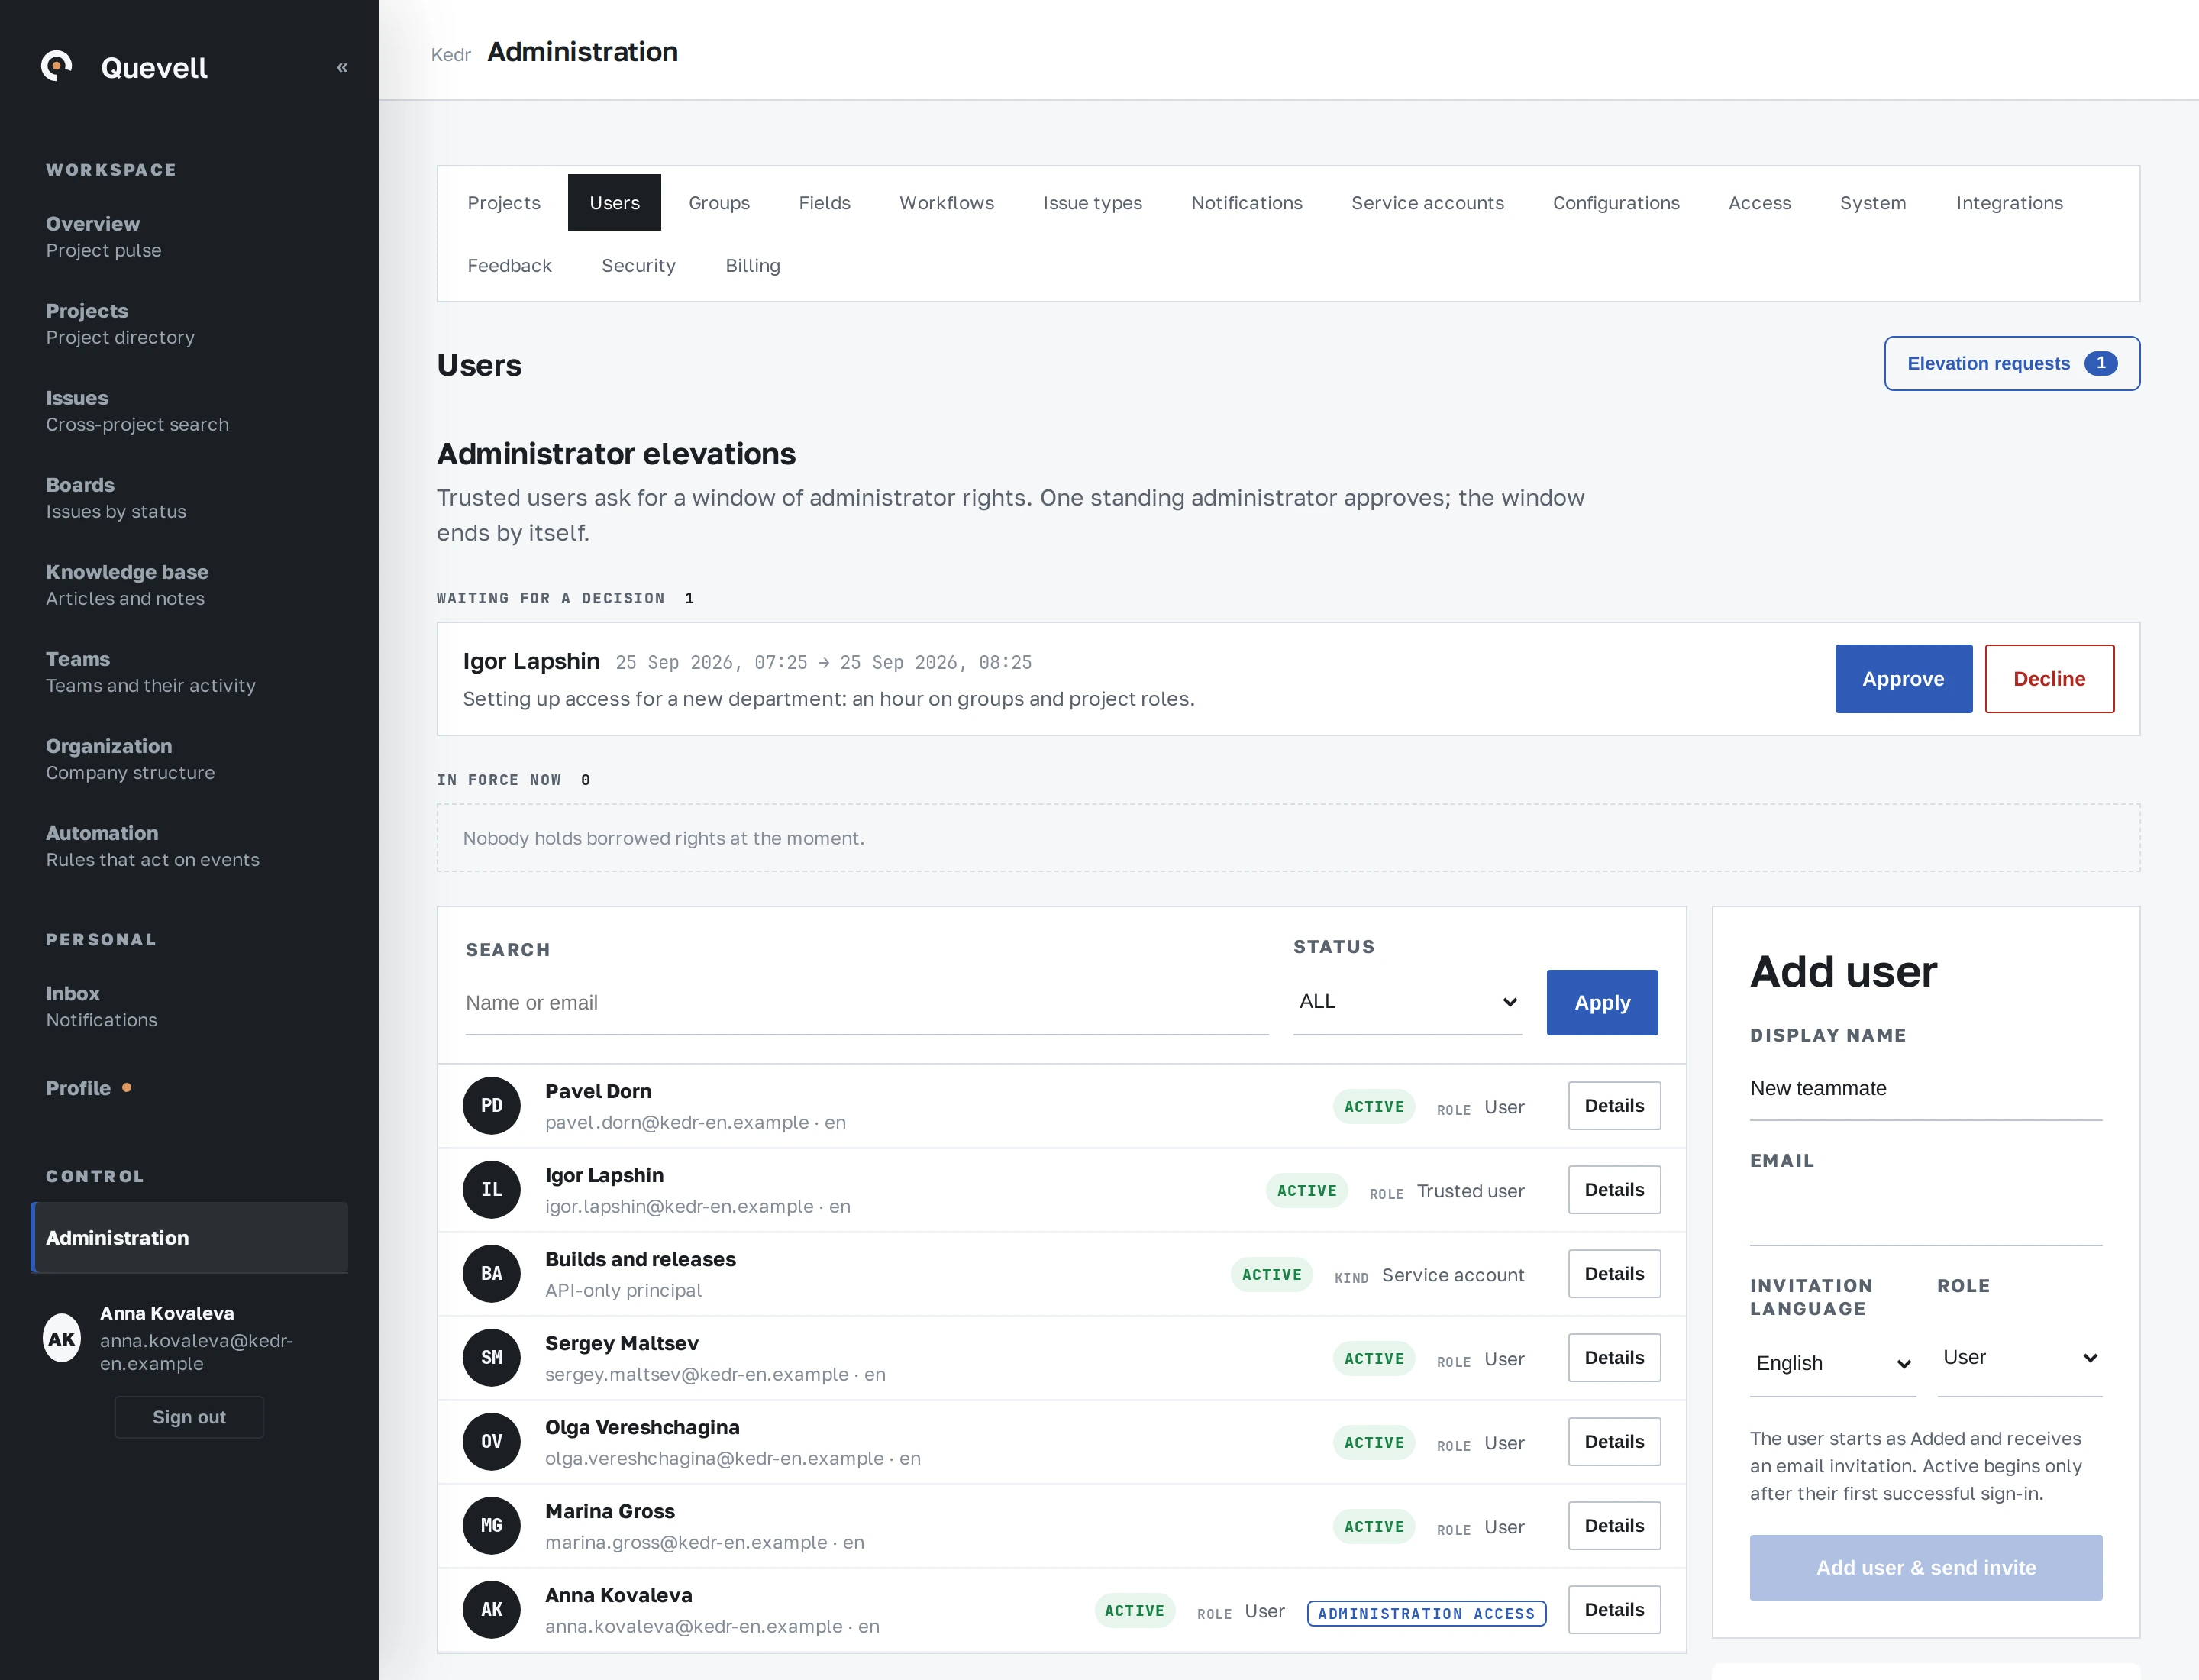
Project roles govern access to work. Issue security narrows that access across search, boards and API calls. Time-limited Administrator rights require a reason and a standing administrator's decision.
Read the documentation
Issue security
Changes and recovery
Issue history records changes to the work. The company audit trail records actions, authors, times and change sets. The application database role cannot update or delete audit records.
A database backup is taken daily. A test restore checks a copy on a separate machine. There is no committed recovery-time SLA.
Data and providers
The current privacy policy places personal-data databases in the Russian Federation. Production traffic uses HTTPS. Sensitive external-call secrets are encrypted at rest; this does not claim that all service data is encrypted at rest.
The subprocessor list is public. The policy and terms specify retention conditions. Issue CSV and page Markdown exports are described separately.
How we treat data
No tracking
No third-party advertising pixels or analytics SDKs, cross-site identifiers, browser fingerprinting or session replay. Client data is not sold or used to train public models.
Try the access model with your team
30 calendar days, up to 10 seats, the full product.